Firewall Services
Managed firewall. Your perimeter, locked down.
Hardware or software firewall for your dedicated server at 151 Front Street West. Managed by Amanah or configured by you. Month-to-month, no contracts. The managed firewall is available on Amanah dedicated servers and on hardware you colocate with us at 151 Front Street West. Managed firewall is quoted with the dedicated server or the rack it protects, rather than as a fixed list price. A managed firewall and DDoS mitigation are separate layers and this page covers the firewall.
Firewall Options
Hardware or software. Your call.
Both options protect your dedicated server from unauthorized access, malicious traffic, and network-level attacks. The right choice depends on your workload, compliance requirements, and how much control you want.
Hardware Firewall
Dedicated Appliance
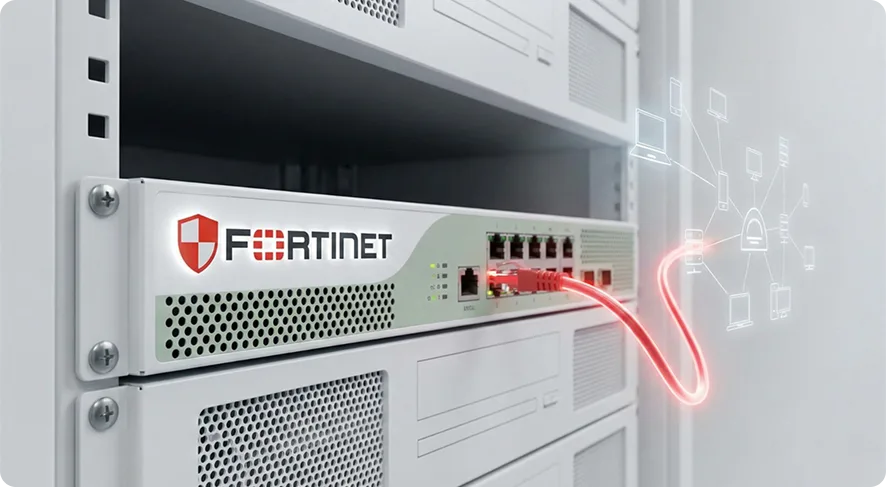
A physical firewall device sits between your server and the network, inspecting and filtering all traffic before it ever reaches your infrastructure. Zero server CPU impact.
WHAT'S INCLUDED
- Dedicated firewall appliance provisioned for your server
- Stateful packet inspection
- Inbound and outbound traffic filtering
- IPsec VPN support
- Intrusion Prevention System (IPS)
- Web filtering and antivirus at the perimeter
- Policy-based rule management
- Can protect multiple servers behind a single appliance
Software Firewall
Host-Based Protection
A software firewall runs directly on your server OS, controlling exactly which connections are allowed in and out at the host level. Highly flexible and immediately deployable.
WHAT'S INCLUDED
- CSF (ConfigServer Firewall) setup and configuration
- iptables / nftables rule management
- Port-level access control (whitelists, blacklists)
- Connection rate limiting
- Email and SMS alerts on suspicious activity
- Compatible with all supported Linux distributions
Management Options
Managed by us. Or managed by you.
Amanah manages your firewall
Our team handles rule creation, ongoing configuration, monitoring, and updates. You tell us what you need protected — we handle the rest. Includes documented change management for compliance purposes. Firewall change requests and incidents follow the same P1 to P4 severity and response targets as every other Amanah managed service.
- Rule setup and ongoing management
- 24/7 alert monitoring and response
- Change requests handled on ticket
- Audit-ready change logs
Self-Managed
You manage your firewall
Full root access. You control the ruleset, port restrictions, and access policies. Amanah provisions the firewall and stays hands-off unless you ask for help. No per-change fees.
- Full administrative access
- Configure rules via CLI or web interface
- Amanah available for support on request
- Upgrade to managed at any time
Capabilities
What firewall protection covers.
Choose the level of involvement that fits your team. Change your mind at any time.
Block unauthorized access
Deny connections from unauthorized IPs, ranges, and geolocations before they reach your server.
DDoS mitigation
Rate limiting and connection throttling to absorb and deflect volumetric attack traffic at the network edge.
Port access control
Restrict which ports are open to the public, to specific IPs, or to your internal network only.
Intrusion prevention
IPS rules detect and block known attack signatures, exploit attempts, and anomalous traffic patterns in real time.
Alerting and logging
Email and SMS alerts on blocked connections, rule violations, and suspicious access patterns. Full traffic logs available on request.
VPN and remote access
IPsec VPN support allows secure remote access to your infrastructure without exposing services to the public internet.
Use Cases
Who needs a firewall
Healthcare and compliance-driven workloads
PIPEDA and PHIPA both require documented network access controls. A managed firewall with audit-ready change logs satisfies those requirements without building your own compliance stack.
SaaS platforms and web applications
Limit public exposure to only the ports your application needs. Everything else — database ports, admin interfaces, internal APIs — stays off the public internet.
VPN providers and high-traffic servers
Hardware firewalls offload inspection work from your server CPU, preserving full compute for your application. Essential for bandwidth-intensive workloads running at 10Gbps or 100Gbps.
Colocation and multi-server environments
A single hardware firewall can protect multiple servers behind it — ideal for colo clients managing several machines at 151 Front Street West under one security perimeter.
FAQs
What is the difference between a hardware and software firewall?
A hardware firewall is a dedicated physical appliance that sits between your server and the network, filtering traffic before it reaches your machine — with no CPU load on your server. A software firewall runs on your server OS (using tools like CSF or iptables) and controls traffic at the host level. Both are effective; hardware firewalls are better suited for high-traffic environments and compliance requirements, while software firewalls offer more granular, application-aware control.
Can one hardware firewall protect multiple servers?
Yes. A single hardware firewall appliance can be placed in front of multiple servers, providing centralized perimeter protection for your entire infrastructure segment. This is a common configuration for colocation clients managing several machines at 151 Front Street West.
Is the firewall managed by Amanah or do I manage it myself?
Your choice. Amanah offers a fully managed option where our team handles rule creation, updates, monitoring, and change management. If you prefer full control, you can self-manage with root or admin access to the firewall. You can switch between managed and self-managed at any time.
Does this replace DDoS protection?
No. They solve different problems. DDoS mitigation absorbs volumetric traffic upstream of your hardware; the managed firewall decides which traffic is allowed to reach a service once it arrives. Most clients run both.
Is a firewall available for colocation clients?
Yes. Hardware firewall services are available for colocation clients at 151 Front Street West. A single appliance can protect your entire colocated infrastructure. Contact our team to discuss placement and configuration options. To learn more, reach out to [email protected] about Amanah ALC.