Data sovereignty is the principle that data is governed by the laws of the country where it is stored, and by the laws of any country whose companies control the infrastructure holding it. Data sovereignty in Canada therefore rests on two facts, not one: the servers have to sit in Canada, and the company operating them has to be a Canadian legal entity. Cloud computing made that easy to forget. It did not make it any less true.
- Residency and sovereignty are different questions. Residency is where the data sits. Sovereignty is whose laws can reach it.
- Jurisdiction follows corporate control, not just geography. Under 18 U.S.C. § 2713, a US provider must produce data in its control “regardless of whether such communication, record, or other information is located within or outside of the United States.”
- A Canadian region of a global cloud gives you residency, not sovereignty. The servers are here. The entity that can be compelled may not be.
- Canada has no single localization law. PIPEDA governs accountability, not geography, which is why the question resurfaces with every new customer and every new tender.
- The durable answer is Canadian in both senses at once: Canadian soil, Canadian operating entity, one answer instead of two claims that happen to line up today.
For most of the last fifteen years, infrastructure decisions were made almost entirely on cost, speed, and convenience. Where a server physically sat felt like an implementation detail, something the cloud abstracted away on your behalf. That framing held up right until a regulator, a customer contract, or a foreign government’s subpoena made it very clear that the physical location, and the nationality of the company operating it, had never stopped mattering.
This is not a compliance checklist. That version of the topic already exists. This is the argument for why location itself, not just the paperwork around it, deserves a seat in your infrastructure decision.
What is data sovereignty, and how is it different from data residency?
Data residency is a fact about geography: which country your servers physically sit in. Data sovereignty is a question about authority: whose laws govern that data, including the laws that reach the company operating the infrastructure. A provider can give you residency without sovereignty. That gap is where nearly all of the confusion in this topic lives.
“Data sovereignty” gets used loosely to cover three related but distinct concepts. Separating them clarifies what you are actually protecting against.
| Concept | What it actually means | The question it answers |
| Data residency | The physical location where data is stored. Satisfied by knowing which country your servers sit in. | Where? |
| Data sovereignty | Which country’s laws govern the data, including the laws that reach the company operating the infrastructure, regardless of where the servers sit. | Under whose authority? |
| Data localization | A legal requirement, imposed by a specific regulator or jurisdiction, that certain categories of data must be stored and processed inside that country’s borders. A rule, not a general principle. | Is it mandatory? |
Residency answers “where.” Sovereignty answers “under whose authority.” Localization answers “am I legally required to.” Most vendor marketing answers the first question and lets you assume it settled the other two.
Why did data sovereignty in Canada become a live issue again?
Three forces pushed data sovereignty back onto the agenda after a decade of being treated as settled: geopolitics turned cross-border legal reach into a business continuity risk, regulators began writing sovereignty requirements directly into procurement rules, and enterprise buyers started asking their vendors the question independently of any compliance framework.
Geopolitics stopped being background noise. Trade disputes, sanctions regimes, and shifting alliances turned “which country’s laws govern my data” from an academic question into a business continuity one. A contract clause that looked purely defensive five years ago now reads as prudent.
Regulators started asking the question directly. Public sector procurement, healthcare authorities, and financial regulators across multiple countries began writing data residency and sovereignty requirements directly into procurement rules rather than leaving them to a vendor’s discretion.
Customers started asking their vendors, not just their regulators. Enterprise security questionnaires now routinely include a data sovereignty question, independent of whatever compliance framework the vendor holds. Buyers want a plain answer, not a footnote.
How can foreign law reach data that is stored in Canada?
Legal jurisdiction attaches to corporate control, not only to geography. A company headquartered in one country can be compelled by that country’s courts or agencies to produce data it controls, even when the servers holding that data sit in a completely different country under a completely different legal system. Physical location does not settle the question on its own.
The clearest example is American. The US CLOUD Act, enacted in March 2018, added a single decisive sentence to the federal code. Under 18 U.S.C. § 2713, a provider of electronic communication or remote computing services must preserve, back up, or disclose customer content and records within its “possession, custody, or control,” and it must do so “regardless of whether such communication, record, or other information is located within or outside of the United States.”
Read that clause carefully. It does not ask where the server is. It asks who controls the data. The mechanism differs by jurisdiction, but the pattern is consistent everywhere: your data’s legal exposure depends on your provider’s corporate nationality and structure, not only on your own address or your server’s rack location.
Does a Canadian region of a global cloud give you data sovereignty?
No. It gives you data residency. A Canadian region operated by a foreign-headquartered company means your data physically sits in Canada, which answers the geography question honestly and completely. It leaves the sovereignty question open, because the corporate entity that can be legally compelled to hand that data over may not be a Canadian entity at all.
This is the single most common misreading in the market, and it is not usually anyone acting in bad faith. Residency is a real and verifiable commitment. It is simply a narrower one than the word “sovereignty” implies, and the two get used interchangeably in procurement conversations where the difference is exactly what matters.
If sovereignty matters to your business, ask two questions rather than one: where is the data physically stored, and who legally owns and operates the company storing it? Both answers have to point at the same jurisdiction for the sovereignty claim to hold.
Who actually needs to care about data sovereignty?
Sovereignty is a real cost to optimize for, not a universal requirement. It matters most for public sector work, healthcare, financial services, and any organization whose own customer contracts specify it. For workloads carrying no personal or regulated data and no contractual obligation, the exposure is genuinely low, and being honest about that is more useful than treating every deployment as equally at risk.
It matters a lot for
- Public sector and government-adjacent organizations, where procurement rules increasingly write sovereignty requirements directly into the tender.
- Healthcare and health-adjacent businesses, where patient data carries both legal and reputational weight if it becomes reachable by a foreign order.
- Financial services and fintech platforms, where regulators in multiple jurisdictions have begun treating data location and control as a systemic risk question rather than a cost line.
- Any business whose customers are asking the question. If your own customer contracts specify sovereignty, the requirement is no longer yours to waive.
It matters less for
- Workloads with no personal or regulated data. A static marketing site or an internal analytics dashboard running on synthetic data carries little sovereignty exposure.
- Businesses with no cross-border regulatory footprint and no customer contracts that specify it.
Know which category your workload falls into before you pay for the stronger guarantee.
What do Canadian data sovereignty laws actually require?
Canada has no single, unified law requiring all data to stay inside its borders. PIPEDA, the federal privacy statute, does not prohibit sending personal information abroad. It regulates accountability instead of geography, which is precisely why the sovereignty question keeps returning rather than being answered once.
The Office of the Privacy Commissioner of Canada puts the obligation plainly: an organization “is responsible for personal information in its possession or custody, including information that has been transferred to a third party for processing,” and must “use contractual or other means to provide a comparable level of protection while the information is being processed by a third party.” The OPC also expects organizations to be transparent with individuals about the possibility of foreign authorities accessing their data. In other words, federal law does not tell you to keep data in Canada. It tells you that you remain answerable for it wherever it goes, and that you have to disclose the exposure.
What sits on top of that federal floor is a patchwork: PHIPA and other provincial health statutes, provincial public sector rules, and a growing number of institutional and procurement policies that go further than the law strictly requires, because those institutions decided sovereignty was worth insisting on for themselves.
That patchwork is why the question resurfaces instead of settling. Each new customer, each procurement cycle, and each regulator can add a sovereignty requirement that was not there before. A business that solved this once by choosing a Canadian region of a foreign cloud may find that the same answer no longer satisfies its next enterprise customer or its next public sector tender.
What does a sovereign data centre in Canada look like?
A genuinely sovereign facility answers the residency question and the sovereignty question with the same fact: it is physically located in Canada and legally controlled by a Canadian entity under Canadian law. Nothing about that combination needs re-litigating when a new requirement appears, because there is only one jurisdiction in the answer.
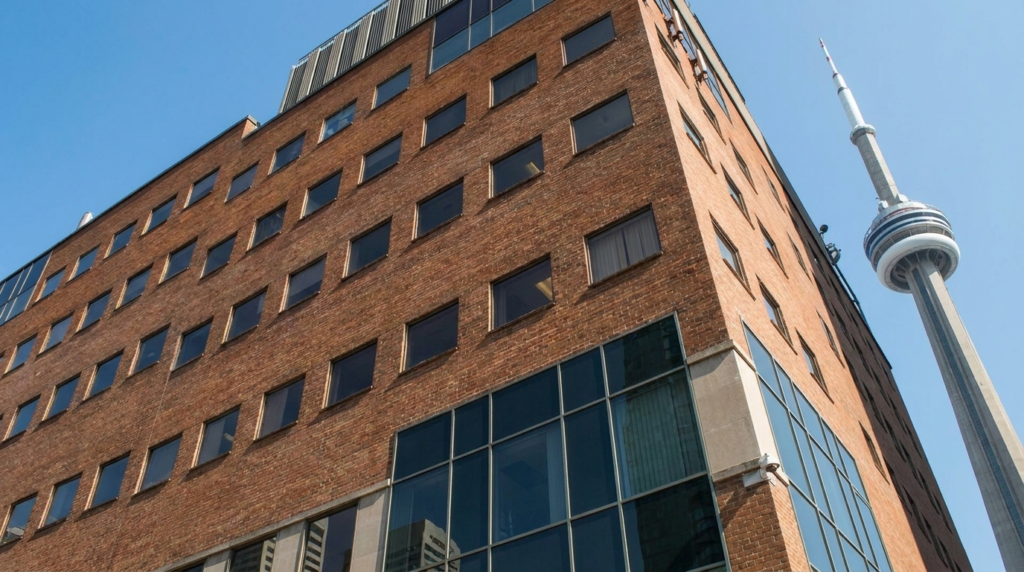
Amanah Tech Inc. is a working example of the pattern. The company was founded in Saskatchewan in 2001, moved to Toronto in 2005, and has never been acquired, merged, or restructured under a foreign parent. It owns and operates two data centres at 151 Front Street West, with all physical infrastructure inside Ontario. When a regulator asks which country’s laws reach the data and which company can be compelled to produce it, both answers are Canadian.
Sovereignty does not require accepting weaker infrastructure to get it. 151 Front Street West is the most connected address in Canada, with more than 400 carriers in the building and direct access to TorIX, the third-largest internet exchange in North America, which peaks above 2.3 Tbps across 312 networks and 270 member organizations. Amanah’s TOR2 facility, opened in 2025, runs on half a megawatt of redundant power with over 100 tons of Enwave deep lake cooling. Its service level agreement guarantees 99.99% monthly availability for both facility power and network, and the company is SOC 2 Type II certified with PIPEDA and PHIPA aligned operations.
That is the argument in one line: Canadian ownership is not a trade-off against connectivity or uptime. It is an additional property that a Canadian-controlled operator can offer and a foreign-controlled one structurally cannot.
How do you evaluate a provider on data sovereignty?
Ask two separate questions and require two separate answers. Where is the hardware physically located, and who legally owns and operates the company running it? If both point at the same country, the sovereignty claim holds. If only one does, you have residency, and the harder question is still open.
Five things worth confirming in writing before you sign:
- The legal entity on the contract. Not the brand, not the regional subsidiary. The incorporated company that would receive a production order.
- The ownership structure above it. A Canadian subsidiary of a foreign parent is a different sovereignty position from a Canadian-owned company, even when both operate the same building.
- The physical address of the facility, and whether the provider owns or resells the space. Ask for a tour. A provider who cannot show you the room is describing someone else’s building.
- Where support, monitoring, and backups run. Data can be resident in Canada while a support desk or backup target abroad still has access to it.
- Independent certification. SOC 2 Type II or equivalent, audited annually, tells you the controls are real rather than asserted.
If sovereignty is the reason you are moving, this is also the moment to reconsider the underlying architecture. Many organizations that start with a sovereignty requirement end up moving workloads off hyperscaler cloud onto dedicated hardware, because predictable cost and a facility they can physically walk into turn out to solve several problems at once. Colocation in Toronto is the usual landing point.
Canadian-owned, Canadian-operated, Canadian jurisdiction.
Talk to us about what that means for your workload, or see the building your data would actually live in.
Questions about this topic
No. Residency is where the data physically sits. Sovereignty is whose laws govern it, which depends on the legal nationality and structure of the company controlling the infrastructure, not just the server’s address. A provider can offer one without the other, and most vendor marketing answers the residency question while leaving sovereignty implied.
Not by itself. If the company operating the Canadian facility is headquartered and legally controlled elsewhere, that company may still be compelled by its home country’s laws to produce data it controls, regardless of where the servers sit. True data sovereignty in Canada requires the operating entity to be Canadian as well as the location.
In cloud computing, data sovereignty is the question of which government can compel your cloud provider to hand over your data. Choosing a Canadian region gives you data residency: the servers are here. It does not change the provider’s corporate nationality, so a foreign-headquartered hyperscaler can still be reached by its home jurisdiction’s legal process.
Federal law does not. PIPEDA regulates accountability rather than geography: organizations stay responsible for personal information transferred to third parties, must use contracts to ensure comparable protection, and must be transparent about possible foreign access. Provincial health statutes such as PHIPA, provincial public sector rules, and individual procurement policies can and do go further.
Three pressures converged. Geopolitical tension made cross-border legal reach a live business risk rather than a theoretical one, regulators started writing sovereignty requirements directly into procurement and licensing rules, and enterprise customers started asking their own vendors the question directly in security reviews.
Ask two separate questions: where is the hardware located, and who legally owns and operates the company running it? If both answers point at the same country, you have a sovereignty claim that holds. If only one does, you have residency and the harder question is still open. Then confirm where support, monitoring, and backups run, since those can reach into Canadian-resident data from abroad.